Available online or onsite, these instructor-led live Threat Detection and Response (TDR) training courses utilize interactive, hands-on exercises to demonstrate how to employ advanced techniques and tools for the real-time identification, analysis, and mitigation of cybersecurity threats.
Threat Detection and Response training is offered as either "online live training" or "onsite live training". Online live training, also referred to as "remote live training", is conducted via an interactive remote desktop. Onsite live training takes place directly on customer premises in Sofia or within NobleProg corporate training centers located in Sofia.
NobleProg -- Your Local Training Provider
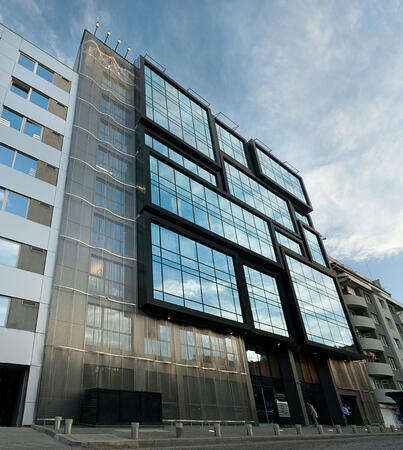
Crystal Business Center
ул. "Осогово" 40, Sofia, Bulgaria, 1303
Crystal Business Center is located in the central part of Sofia, on the corner of "Osogovo" street. and "Todor Aleksandrov" blvd. The building is easily accessible by metro (only 50 m from Opalchenska station) and other public transport. Its total area is 8000 sq.m. The office area is 6171 sq.m.
This instructor-led, live training in Sofia (online or onsite) is designed for intermediate-level cybersecurity professionals looking to implement CTEM within their organizations.
By the conclusion of this training, participants will be equipped to:
Grasp the core principles and stages of CTEM.
Identify and prioritize risks using established CTEM methodologies.
Seamlessly integrate CTEM practices into current security protocols.
Leverage tools and technologies for ongoing threat management.
Develop strategies to continuously validate and enhance security measures.
This instructor-led, live training in Sofia (online or onsite) is aimed at intermediate-level cybersecurity professionals who wish to leverage DeepSeek for advanced threat detection and automation.
By the end of this training, participants will be able to:
Utilize DeepSeek AI for real-time threat detection and analysis.
Implement AI-driven anomaly detection techniques.
Automate security monitoring and response using DeepSeek.
Integrate DeepSeek into existing cybersecurity frameworks.
Participate in this instructor-led training in Sofia to gain proficiency in OpenEDR basics. Acquire skills in deploying agents, setting up telemetry, and evaluating endpoint events for threat identification. Practical labs in Sofia emphasize incident response and the integration of alerts into security operations.
This advanced program in Sofia empowers SOC analysts and threat hunters with the practical expertise needed to deploy OpenEDR and integrate it seamlessly with MITRE ATT&CK. Learners will develop the ability to craft detection logic, execute strategic hunting workflows, and conduct root cause analysis to bolster their organization's security posture.
This instructor-led training in Sofia empowers security professionals with advanced ransomware negotiation strategies and threat intelligence expertise. Participants will dissect attack lifecycles, engage in simulated negotiations, and operationalize intelligence for robust defense.
This instructor-led, live training in Sofia (online or onsite) is designed for advanced cyber security professionals who wish to understand Cyber Threat Intelligence and develop skills to effectively manage and mitigate cyber threats.
By the end of this training, participants will be able to:
Understand the fundamentals of Cyber Threat Intelligence (CTI).
Analyze the current cyber threat landscape.
Collect and process intelligence data.
Perform advanced threat analysis.
Leverage Threat Intelligence Platforms (TIPs) and automate threat intelligence processes.
This live, instructor-led training in Sofia supports beginner-level cybersecurity professionals in mastering detection engineering. Learners will acquire the ability to create effective rules, analyze logs, utilize threat intelligence, and refine alerts to lower false positives within a contemporary SOC workflow.
Live, instructor-led training in Sofia designed for IT security professionals. Master the skills to plan, categorize, contain, and manage incidents through practical simulations. Enhance your organization's response capabilities by developing hands-on expertise in detection, eradication, and recovery strategies.
This advanced training in Sofia empowers security researchers with the expertise to automate workflows and scale reconnaissance for bug bounty hunting. Learners will master detecting high-impact vulnerabilities, developing custom scripts, and efficiently managing complex targets.
This instructor-led live training in Sofia provides beginners with the essential skills for ethical bug hunting. It covers the use of key tools like Burp Suite and addresses common vulnerabilities such as XSS, SQLi, and CSRF, enabling participants to effectively identify flaws and produce clear, professional reports.
This instructor-led live training in Sofia (available online or onsite) is tailored for intermediate-level duty managers and operational leaders who aim to develop robust cyber resilience strategies to safeguard their organizations against cyber threats.
By the end of this training, participants will be able to:
Understand the core concepts of cyber resilience and their application to duty management.
Develop incident response plans to maintain operational continuity.
Identify potential cyber threats and vulnerabilities within their environment.
Implement security protocols to minimize risk exposure.
Coordinate team response during cyber incidents and recovery processes.
This instructor-led, live training in Sofia (online or on-site) is designed for IT security professionals at an intermediate level who wish to develop skills in security monitoring, analysis, and response.
Upon completion of this training, participants will be able to:
Comprehend the role of the Blue Team within cybersecurity operations.
Utilize SIEM tools for security monitoring and log analysis.
Identify, analyze, and respond to security incidents.
Conduct network traffic analysis and gather threat intelligence.
Implement best practices in Security Operations Center (SOC) workflows.
This instructor-led, live training in Sofia (online or onsite) is aimed at intermediate-level to advanced-level cybersecurity professionals who wish to elevate their skills in AI-driven threat detection and incident response.
By the end of this training, participants will be able to:
Implement advanced AI algorithms for real-time threat detection.
Customize AI models for specific cybersecurity challenges.
Develop automation workflows for threat response.
Secure AI-driven security tools against adversarial attacks.
This instructor-led, live training in Sofia (online or onsite) is designed for beginner-level cybersecurity professionals eager to learn how to utilize AI for enhanced threat detection and response capabilities.
Upon completion of this training, participants will be able to:
Grasp AI applications within cybersecurity.
Deploy AI algorithms for threat identification.
Automate incident response using AI tools.
Incorporate AI into current cybersecurity infrastructure.
This vendor-neutral CHFI training in Sofia builds essential digital forensics skills, covering evidence collection, chain-of-custody, and advanced analysis techniques. It prepares professionals to handle digital evidence for litigation and corrective actions using hands-on labs.
This instructor-led, live training in Sofia (online or onsite) covers various aspects of enterprise security, from AI to database security. It also includes the latest tools, processes, and mindset needed to protect against attacks.
This instructor-led, live training in Sofia (online or onsite) is designed for information system analysts looking to leverage MITRE ATT&CK to reduce the likelihood of a security breach.
Upon completion of this training, participants will be able to:
Establish the required development environment to begin implementing MITRE ATT&CK.
Categorize how attackers interact with systems.
Document adversary behaviors within systems.
Monitor attacks, identify patterns, and evaluate existing defense tools.
It did give me the insight what I needed :) I am starting teaching on a BTEC Level 3 qualification and wanted to widen my knowledge in this area.
Otilia Pasareti - Merthyr College
Course - Fundamentals of Corporate Cyber Warfare
- Understanding that ATT&CK creates a map that makes it easy to see, where an organization is protected and where the vulnerable areas are. Then to identify the security gaps that are most significant from a risk perspective.
- Learn that each technique comes with a list of mitigations and detections that incident response teams can employ to detect and defend.
- Learn about the various sources and communities for deriving Defensive Recommendations.
Online Threat Detection and Response (TDR) training in Sofia, TDR training courses in Sofia, Weekend TDR courses in Sofia, Evening Threat Detection and Response training in Sofia, Threat Detection and Response (TDR) instructor-led in Sofia, TDR (Threat Detection and Response) coaching in Sofia, Online TDR training in Sofia, Threat Detection and Response instructor-led in Sofia, TDR classes in Sofia, TDR private courses in Sofia, Threat Detection and Response (TDR) instructor in Sofia, Threat Detection and Response trainer in Sofia, TDR one on one training in Sofia, Threat Detection and Response (TDR) on-site in Sofia, Evening TDR courses in Sofia, Weekend TDR training in Sofia, TDR boot camp in Sofia